Compliance & Fraud
Identity Verification (KYC)
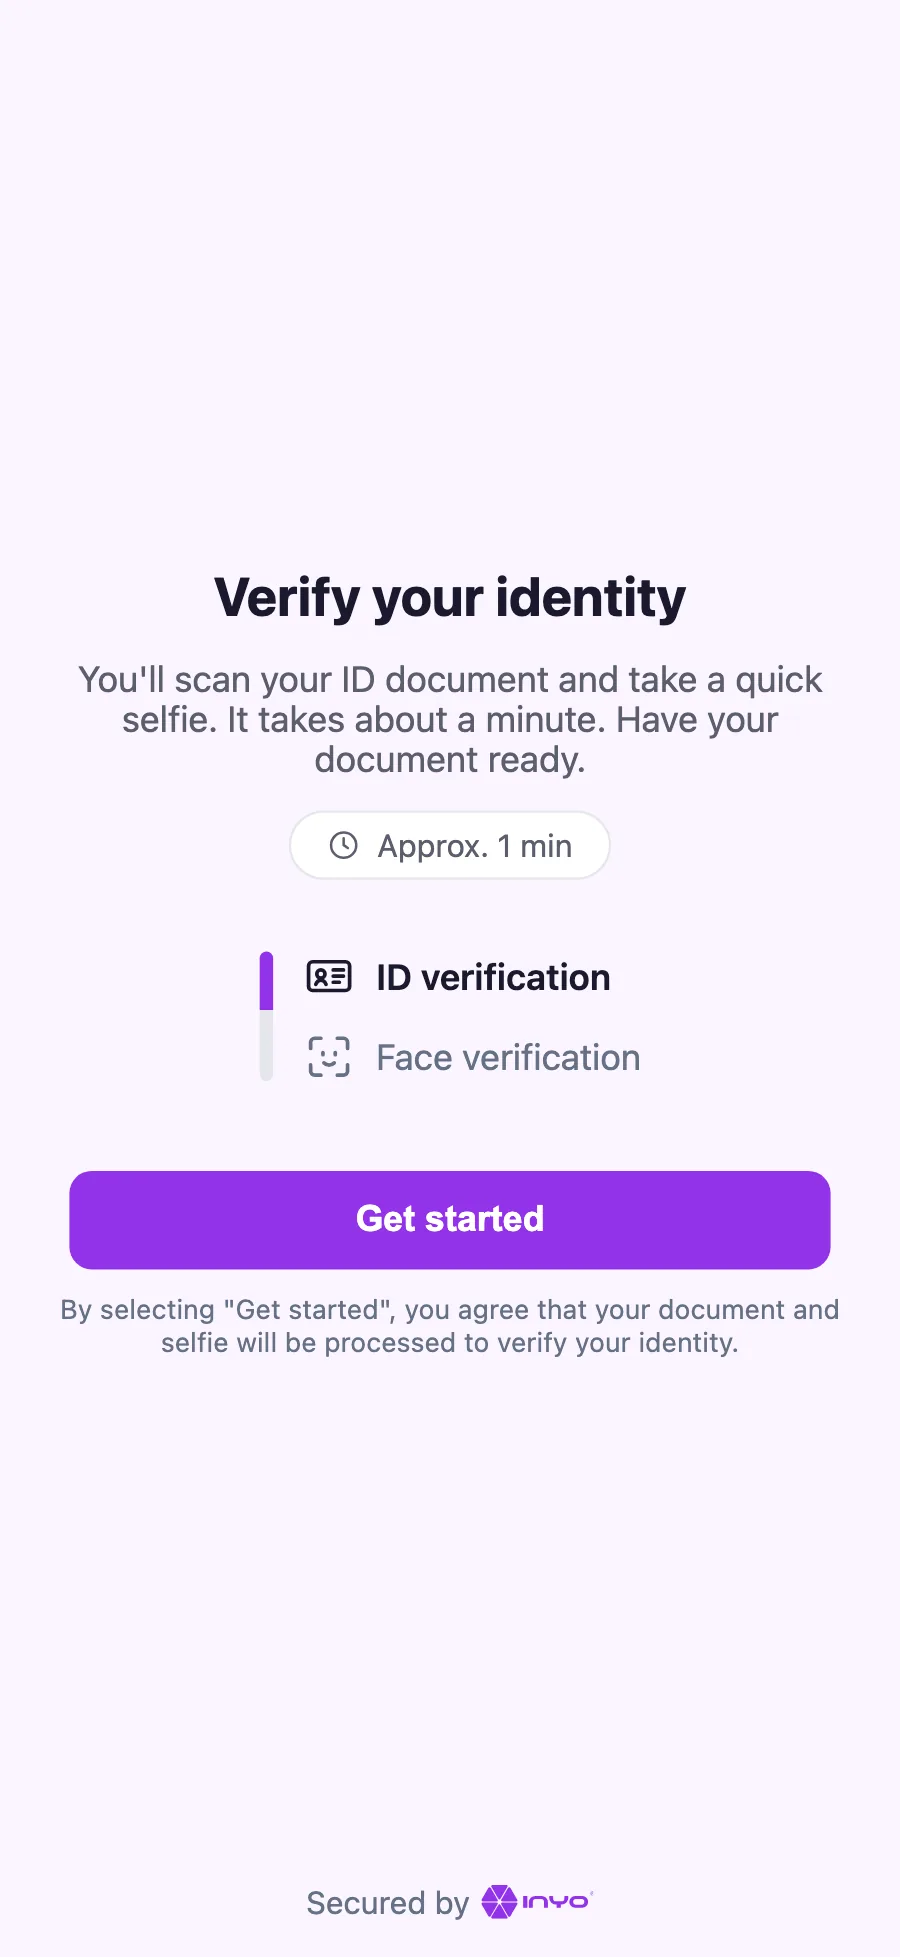
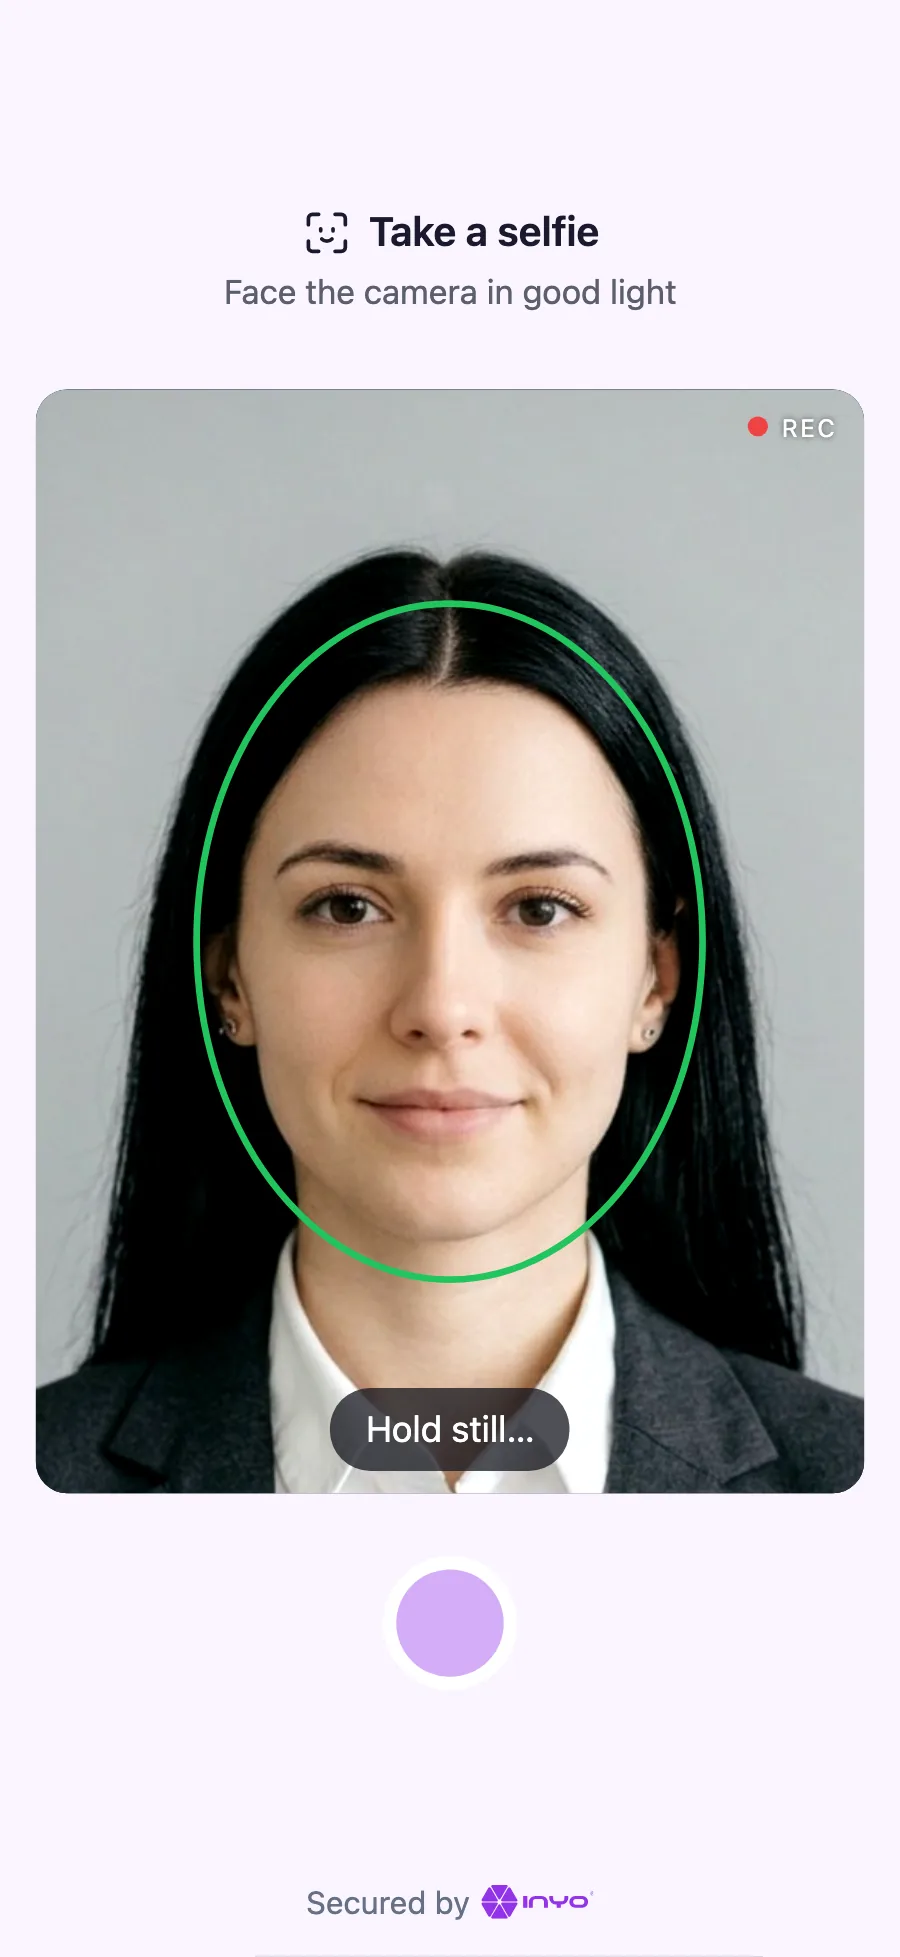
Know your customer is who they say they are. In Inyo360's hosted widget the customer photographs a government ID and takes a selfie; Inyo360 verifies the document, confirms a live person who matches its portrait, and weighs every other signal it holds, returning one result you can act on.
A real, readable document
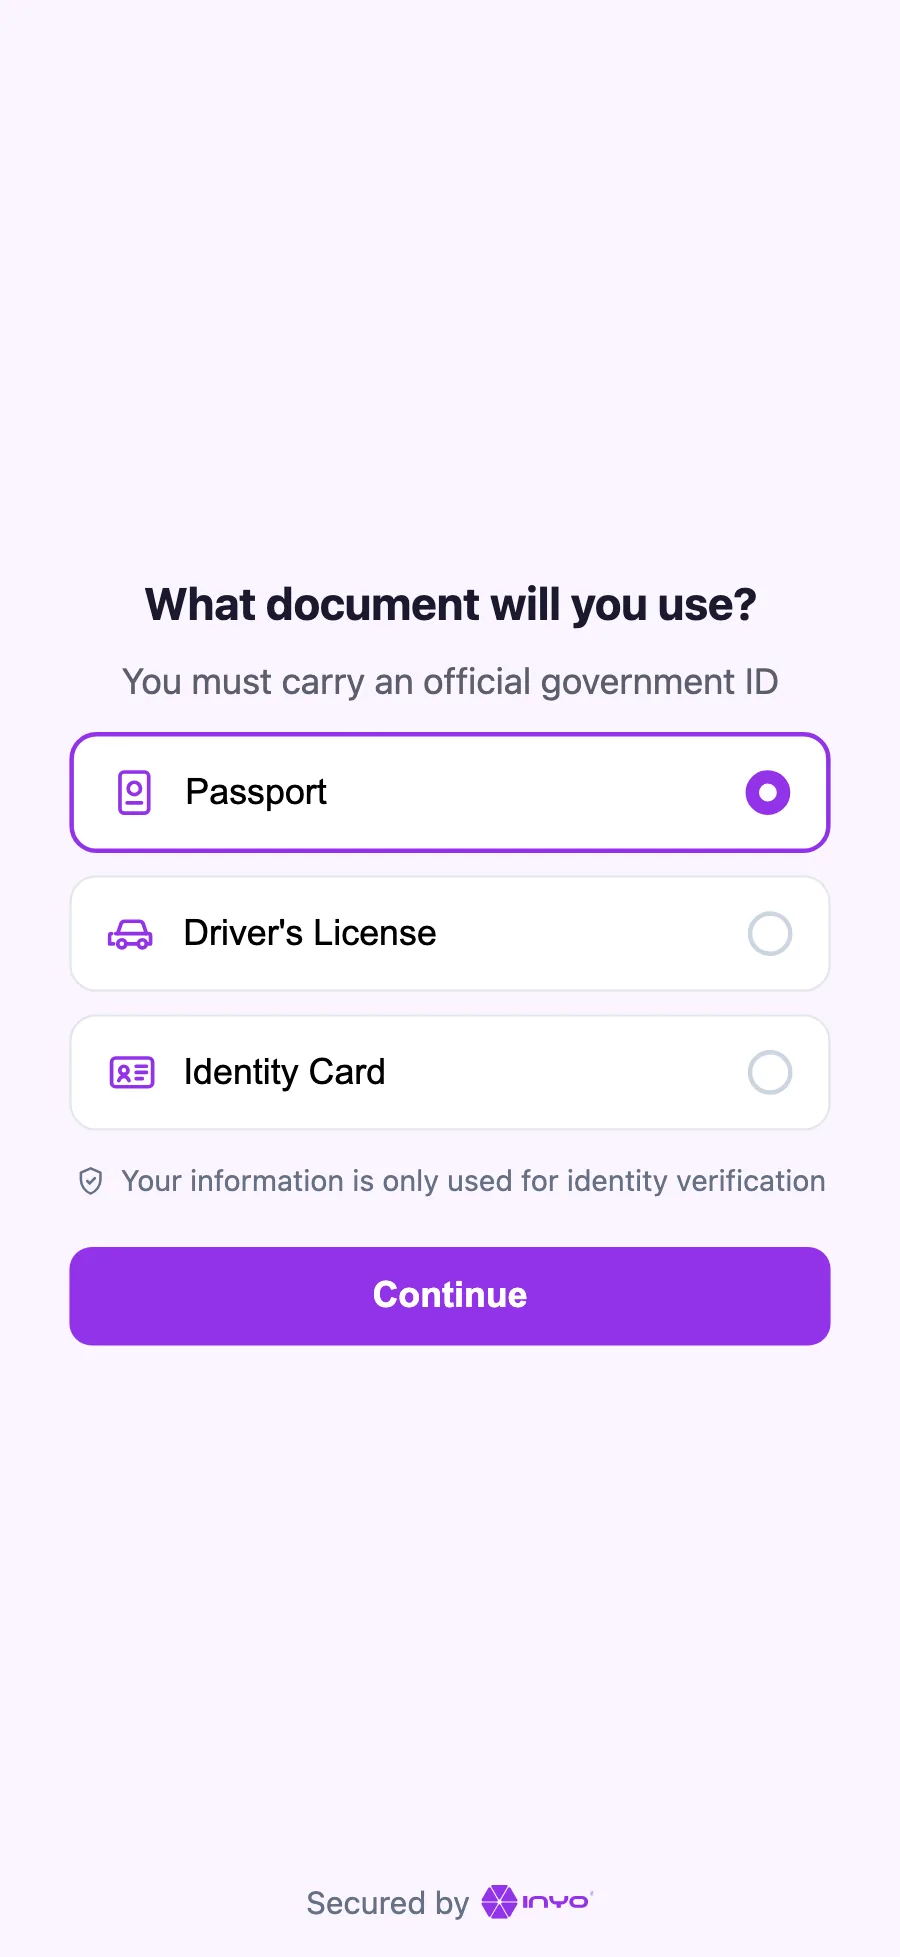
Passports, driver's licenses and identity cards are read and checked for authenticity and expiry, with their machine-readable zone and barcode decoded. Documents
A live face, matched to the ID
Liveness confirms a real person in front of the camera, and the face is matched against the document portrait. Biometrics
Beyond the document
The data you already hold, the phone and its carrier, sanctions lists, and the device and its connection are all weighed in the same session. Signals & Checks
One result to act on
Every check, a trust index from 0 to 100 and, under managed decisioning, a decision, delivered by signed webhook or redirect. Session Results
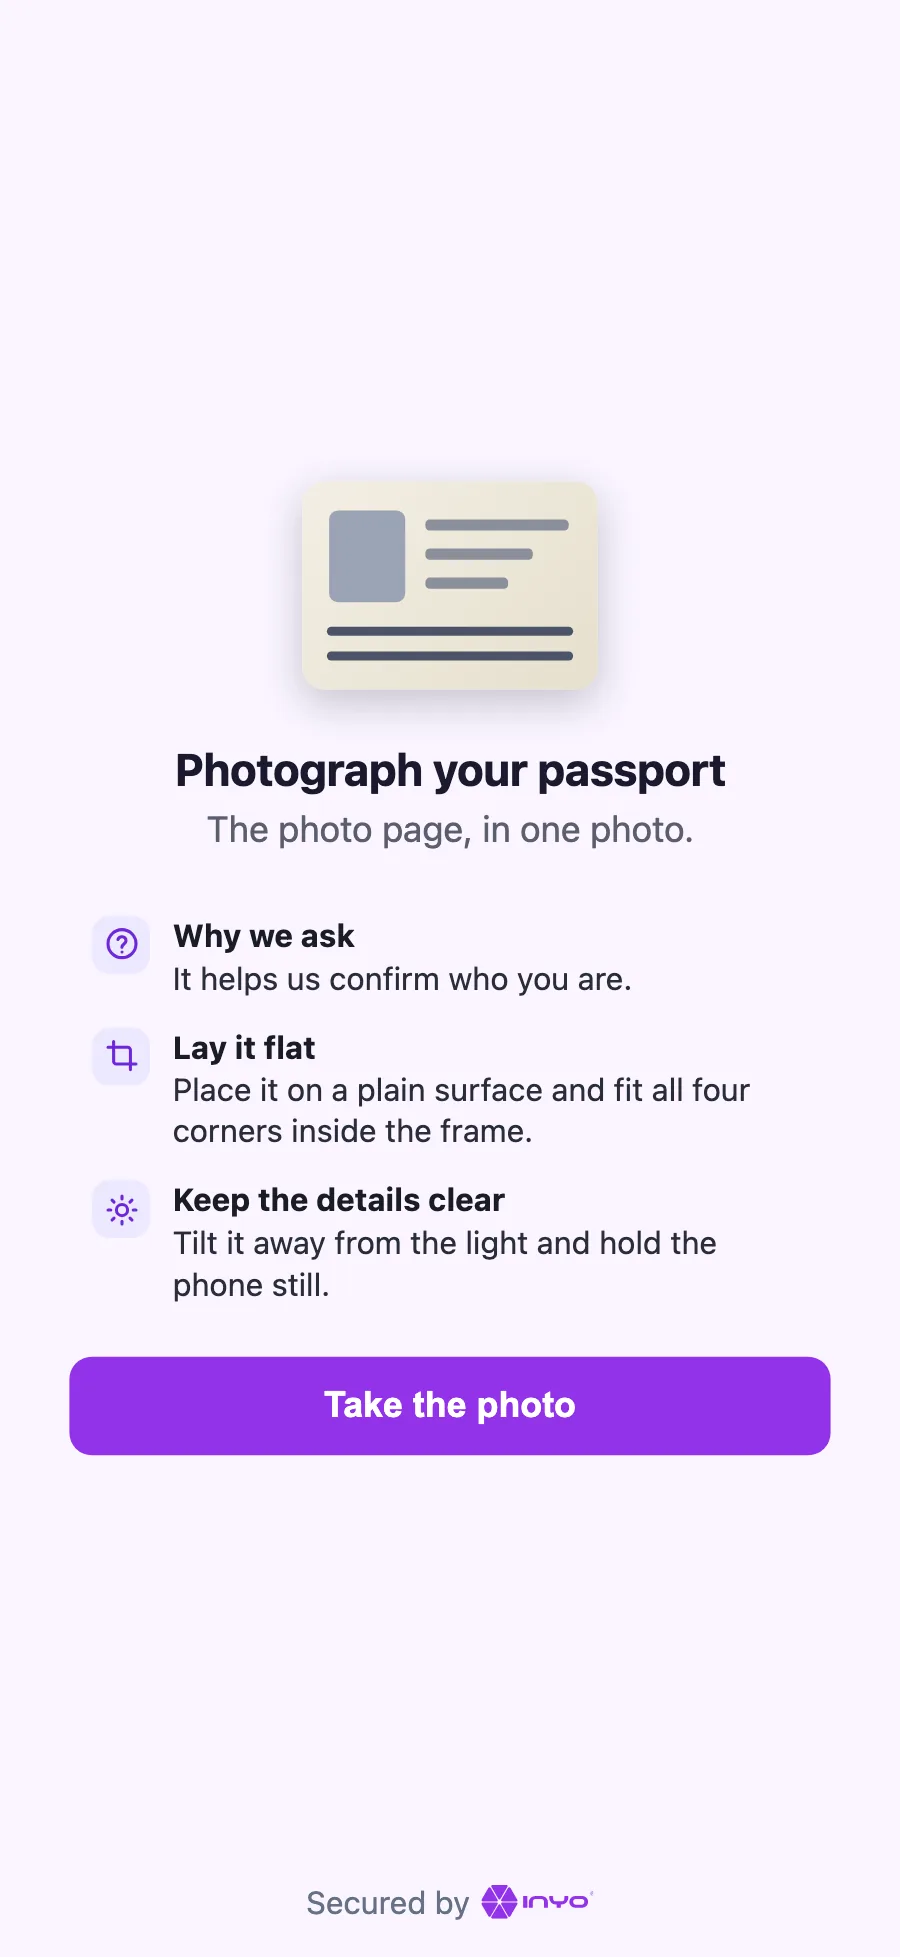
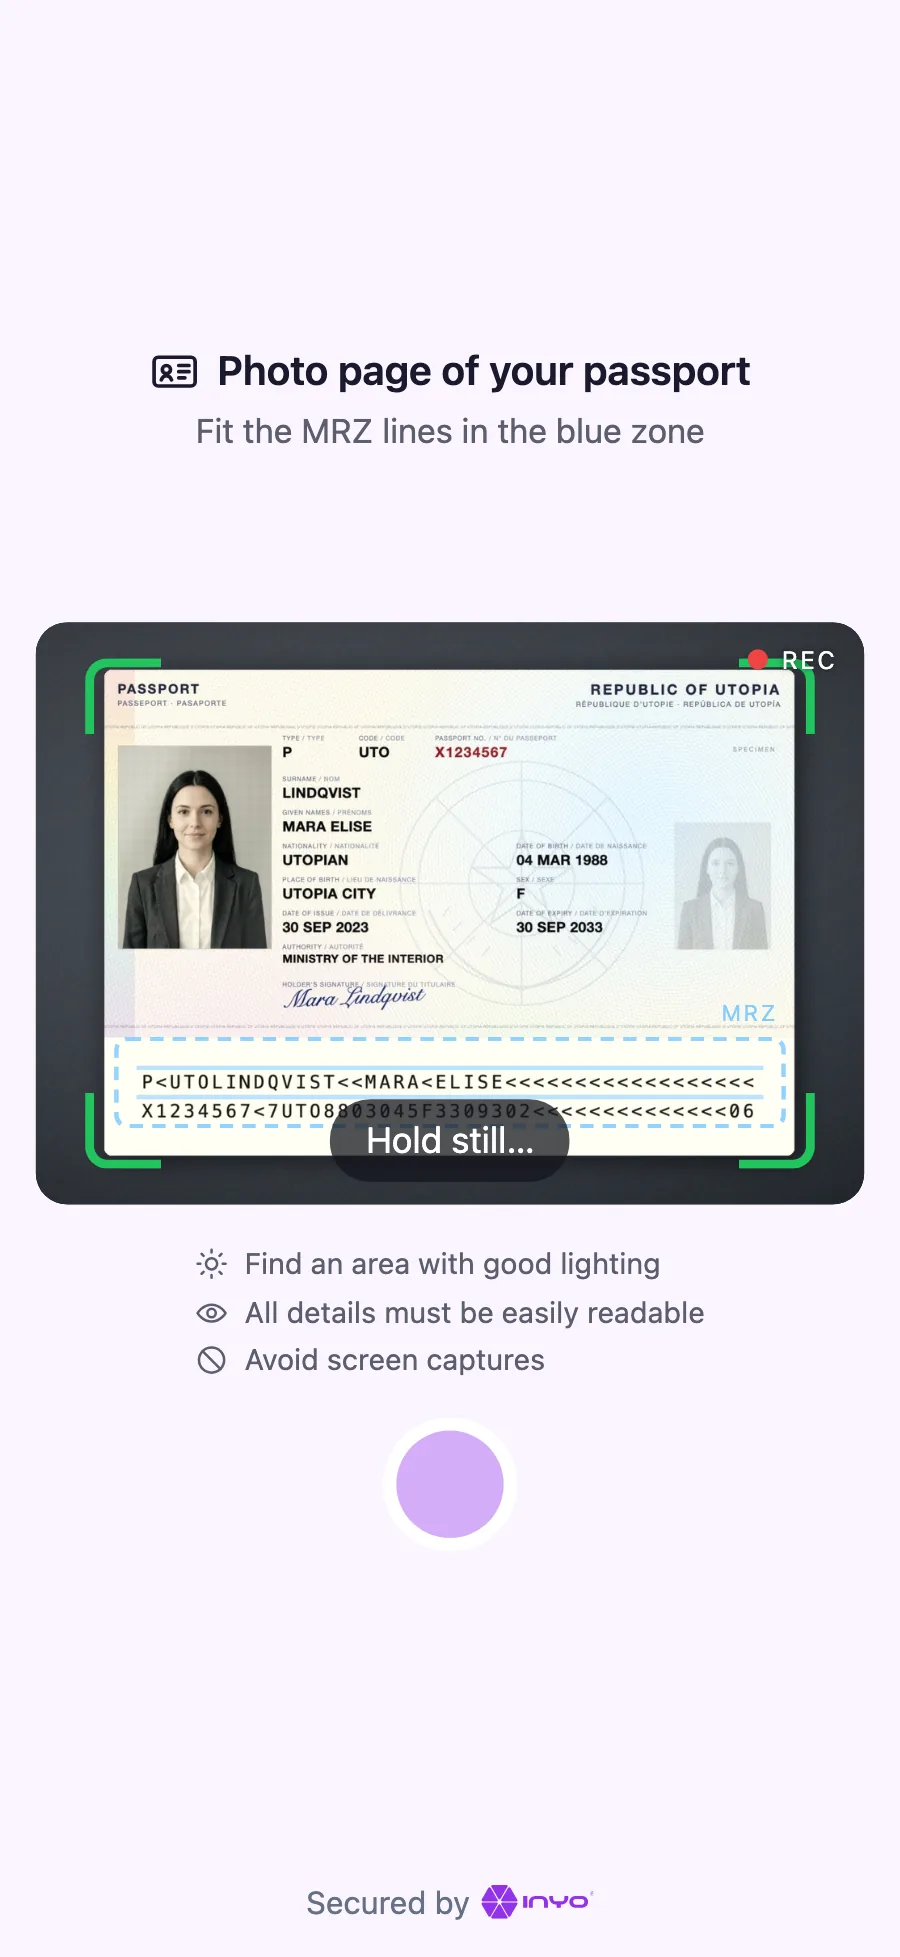
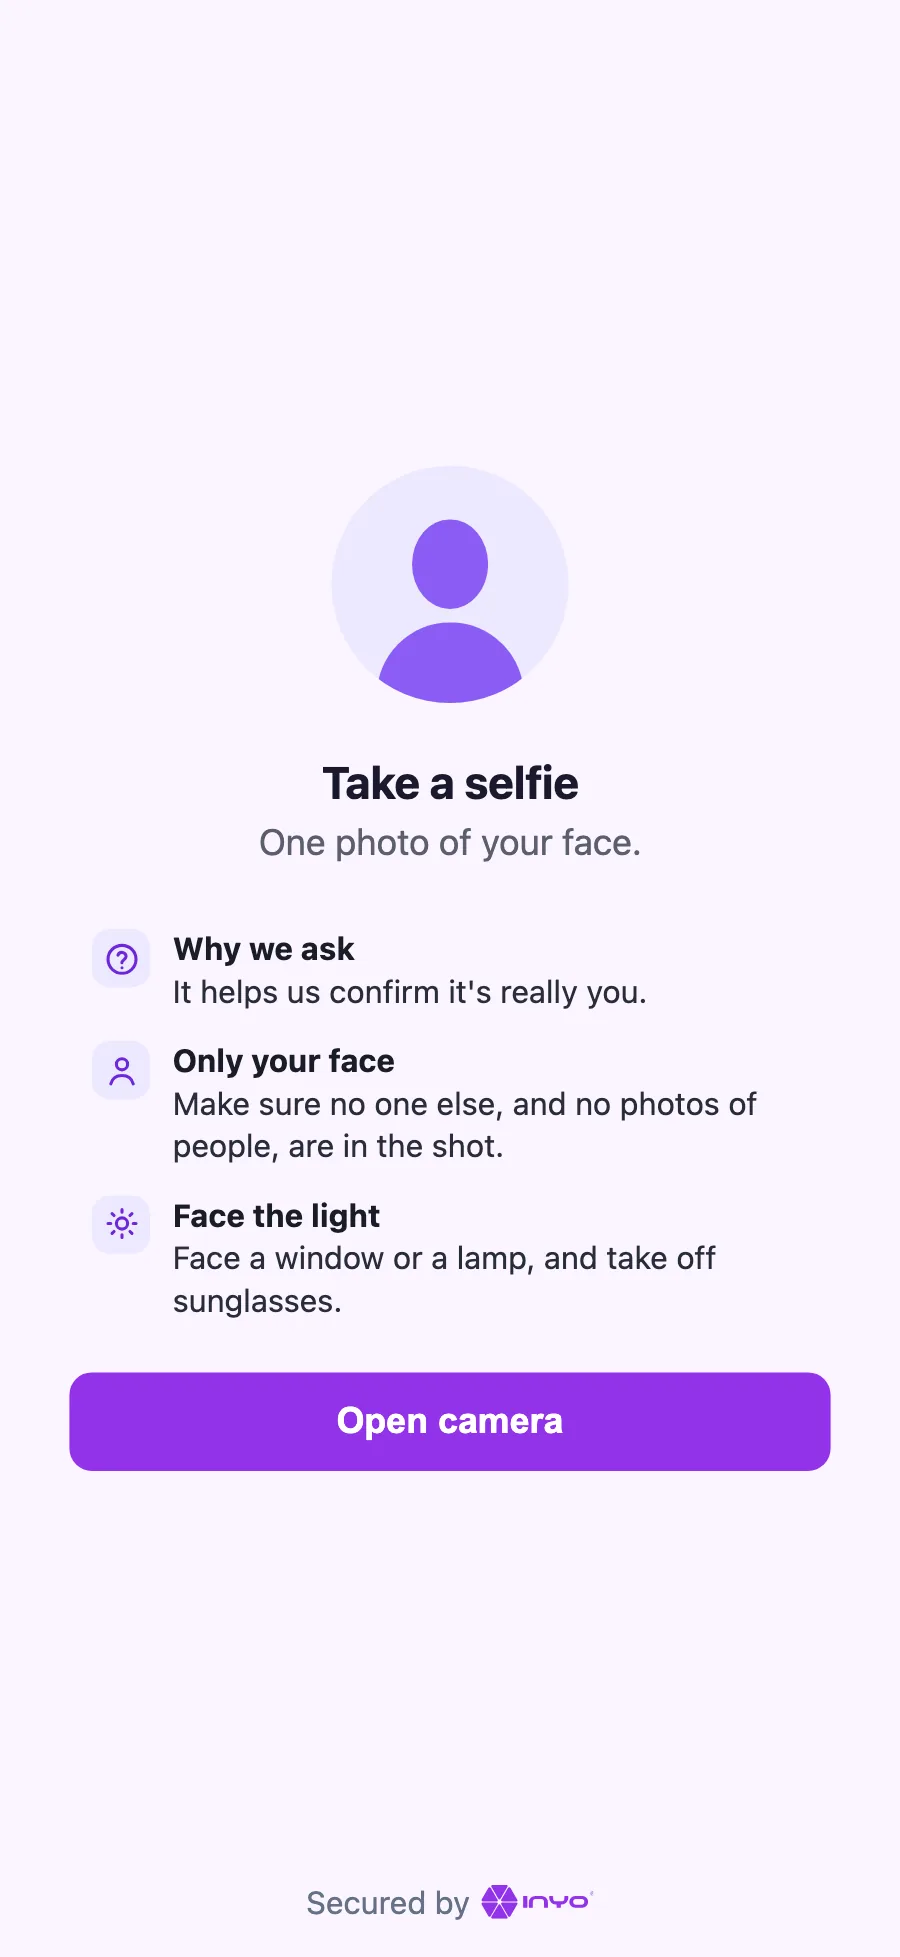
Two Ways to Integrate
Choose one per verification — both produce the same normalized result and honor the same configuration.
| Mode | How it works | Choose this when |
|---|---|---|
| Hosted widget | You create a session and receive a widgetUrl. Send it to your customer or open it in a webview. Inyo360 handles camera capture, framing guidance, retries, and localization. | You want the fastest integration and no camera code of your own. This is the recommended default. |
| Server-to-server | You capture the images yourself and post them to POST /v1/verifications. The call is accepted immediately; the outcome arrives by webhook or is read back. | You already have a capture UI, or verification happens without a live customer (for example, re-verifying stored documents). |
What Each Path Gives You
Server-to-server runs the full Inyo360 verification engine on the images you send. The hosted widget runs the same engine and adds everything that happens while the customer is holding the camera.
| Server-to-server The full engine on the images you send | Hosted widget The same engine, plus live capture | |
|---|---|---|
| The full verification engine, in both Same checks, same configuration, same result | ||
| Passports, driver’s licenses and identity cards checked for authenticity, type and expiry |  | |
| MRZ and barcode decoded and checked against the printed data | | |
| Identity data compared with the document and with what you already hold | | |
| The phone line checked with the carrier: the kind of line, such as VoIP, and whether it is registered to the person | | |
| The selfie matched to the document portrait | | |
| Age estimation consistent with the document’s date of birth | | |
| The name screened against sanctions lists | | |
| US driver’s licenses matched against the issuing DMV’s records | | |
| Documents limited to the issuing countries you accept | | |
| Every signal counts toward one trust score | | |
| Optional managed decisioning and manual review | | |
| Added by the hosted widget What live capture makes possible | ||
| No camera code to build or maintain |  | |
| Live framing and glare guidance | | |
| Customer retries an unusable capture on the spot | | |
| Localized capture screens | | |
| Liveness confirmed as the selfie is taken, not from a photo or a screen | | |
| The device recognised across visits, by an identifier that persists | | |
| Device data: tampered browser environments and identifications replayed from another session | | |
| Behavioral data: sessions driven by automation rather than by a person | | |
| Geolocation: connections routed through VPNs, proxies, anonymising networks or hosting providers | | |
| Payment card verification add-on, in the same session | | |
| Guided capture and selfie clips as compliance evidence | | |
| Signed redirect back to your app | | |
Included Not part of this path
When server-to-server is the right fit
You already own a capture UI, or you verify documents you already hold with no customer present. You get every check in the engine above and the same result your widget sessions would produce.
How It Works
sequenceDiagram
    autonumber
    participant Y as Your System
    participant I as Inyo360
    participant C as Customer
    Y->>I: POST /v1/sessions
    I-->>Y: sessionId +<br/>widgetUrl
    Y->>C: deliver widgetUrl
    C->>I: document<br/>front / back
    C->>I: selfie + liveness
    Note over I: Run verification<br/>checks
    I-->>Y: signed webhook<br/>or redirect
    Y->>I: GET /v1/sessions/{id}
    I-->>Y: assessment,<br/>and a decision<br/>if managed
    Y->>C: show outcome
Integration Steps
| Step | Action | Endpoint | Description |
|---|---|---|---|
| 1 | Authenticate | POST /oauth/token | Exchange your client credentials for a Bearer token |
| 2 | Create a session | POST /v1/sessions | Returns a sessionId and a widgetUrl |
| 3 | Deliver the widget | — | Send the link, or open it in a webview |
| 4 | Receive the result | your webhookUrl | A signed POST of the verification result |
| 5 | Read the result | — | Interpret status, checks[], trustIndex, and decision if you have it |
| 6 | Confirm server-side | GET /v1/sessions/{sessionId} | The authoritative record for a single widget session. A server-to-server verification is read at GET /v1/verifications/{verificationId} |
Skipping the widget? Replace steps 2-4 with a server-to-server verification, and read step 6 at GET /v1/verifications/{verificationId}.
What You Receive
Every verification resolves to one normalized result containing the extracted document and person data, the individual checks, and — under managed decisioning — the decision:
{
  "sessionId": "…",
  "userRef": "user-123",
  "status": "completed",
  "decision": "approved",
  "document": { "type": "passport", "number": "…", "expirationDate": "2033-09-30" },
  "person": { "firstName": "…", "lastName": "…", "dateOfBirth": "1988-03-04" },
  "checks": [
    { "name": "document_not_expired", "status": "passed", "group": "document", "severity": "critical", "detail": "…" },
    { "name": "face_match", "status": "passed", "group": "selfie", "severity": "high", "detail": "similarity vs threshold 90.0" }
  ],
  "provider": "inyo",
  "trustIndex": 100,
  "completedAt": "2026-07-31T14:04:57.874Z"
}
What that result concludes depends on your decisioning mode. Under non-managed decisioning — the default — Inyo360 publishes the assessment and you decide. Under managed decisioning Inyo360 also reaches a verdict, delivered as decision: approved, declined, inconclusive, or in_review while a person looks at it.
The full payload and the rules for reading it are on Session Results.
Architecture Pattern
Your OAuth credentials are server-side only. Create sessions from your backend and hand the customer only the returned widgetUrl — it carries a single-use, time-limited code and grants access to nothing but that one verification.
flowchart TB
    subgraph browser["Customer's device"]
        C["Browser /<br/>webview"]
    end
    subgraph yours["Your infrastructure"]
        S["Your server<br/>holds OAuth credentials"]
    end
    subgraph inyo["Inyo360"]
        W["Hosted widget"]
        A["Tenant API"]
    end
    S -->|"POST /v1/sessions<br/>Bearer token"| A
    A -->|"widgetUrl"| S
    S -->|"widgetUrl only"| C
    C -->|"document + selfie"| W
    W --> A
    A -->|"signed result"| S
Environments
| Resource | URL |
|---|---|
| Tenant API (sandbox) | https://{FQDN} |
| Tenant API (production) | https://{FQDN} |
| Widget host | https://{FQDN} |
Base URLs, OAuth client credentials, and IP allowlisting are issued by Inyo during onboarding. Sandbox and production credentials are not interchangeable.
Next Steps
| Page | What it covers |
|---|---|
| Getting Started | Run one verification end to end |
| Authentication | Tokens, scopes, and error handling |
| Verification Sessions | Every field on POST /v1/sessions |
| Receiving Results | Signature verification and delivery modes |
| Manual Review | Handling an in_review decision correctly |
| Sandbox & Test Data | Testing before you go live |